October 2, 2026

SC-100 Dumps By Pros – 1st Attempt Guaranteed Success [Q114-Q136]

Rate this post

SC-100 Dumps By Pros – 1st Attempt Guaranteed Success

100% Guarantee Download SC-100 Exam Dumps PDF Q&A

Microsoft SC-100 Certification Exam is a great way for professionals to demonstrate their expertise in cybersecurity architecture. Microsoft Cybersecurity Architect certification offers a competitive edge to individuals who are seeking employment opportunities in the cybersecurity industry. It is also beneficial for professionals who wish to advance their careers within their current organizations.


Q114. You have three Microsoft Entra tenants named Tenant 1. Tenant2. and Tenant3.
You have three Azure subscriptions named Sub1, Sub2, and Sub3. Each tenant is associated with multiple Azure subscriptions.
Each subscription contains a single Microsoft Sentinel workspace as shown in the following table.

You need to recommend a solution that meets the following requirements:
* Ensures that the users in Tenant1 can manage the resources in Sub2 and Sub3 without having to switch subscriptions or sign in to a different tenant
* Implements multiple workspace view for Sentinel2 and Sentinel3
What should you use to delegate permissions, and which Microsoft Sentinel feature will users be able to manage in multiple workspace view? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q115. You use Azure Pipelines with Azure Repos to implement continuous integration and continuous deployment (CI/CO) workflows.
You need to recommend best practices to secure the stages of the CI/CD workflows based on the Microsoft Cloud Adoption Framework for Azure.
What should you include in the recommendation for each stage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q116. You have a Microsoft 365 tenant.
You need to recommend a Microsoft 365 Defender solution to enhance security for the tenant. The solution must meet the following requirements:
* Identify users that are downloading an unusually high number of files from Microsoft SharePoint Online sites and are possibly involved in a data exfiltration attempt.
* Block Microsoft Teams messages that contain potentially malicious content by using zero-hour auto purge (ZAP).
What should you recommend for each requirement? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Q117. Your company, named Contoso. Ltd… has an Azure AD tenant namedcontoso.com. Contoso has a partner company named Fabrikam. Inc. that has an Azure AD tenant named fabrikam.com. You need to ensure that helpdesk users at Fabrikam can reset passwords for specific users at Contoso. The solution must meet the following requirements:
* Follow the principle of least privilege.
* Minimize administrative effort.
What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Q118. You plan to deploy a dynamically scaling, Linux-based Azure Virtual Machine Scale Set that will host jump servers. The jump servers will be used by support staff who connect f personal and kiosk devices via the internet. The subnet of the jump servers will be associated to a network security group (NSG) You need to design an access solution for the Azure Virtual Machine Scale Set. The solution must meet the following requirements:
* Ensure that each time the support staff connects to a jump server; they must request access to the server.
* Ensure that only authorized support staff can initiate SSH connections to the jump servers.
* Maximize protection against brute-force attacks from internal networks and the internet.
* Ensure that users can only connect to the jump servers from the internet.
* Minimize administrative effort
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q119. Hotspot Question
Your company uses Microsoft Defender for Cloud and Microsoft Sentinel.
The company is designing an application that will have the architecture shown in the following exhibit.
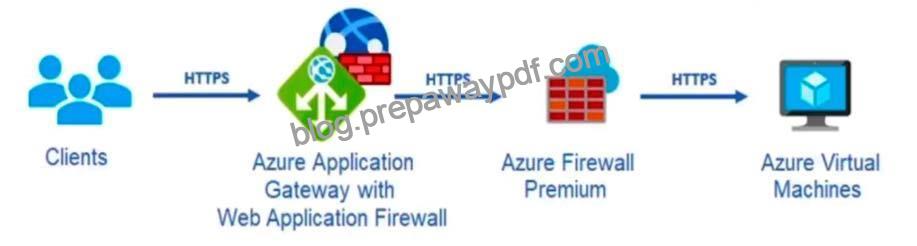
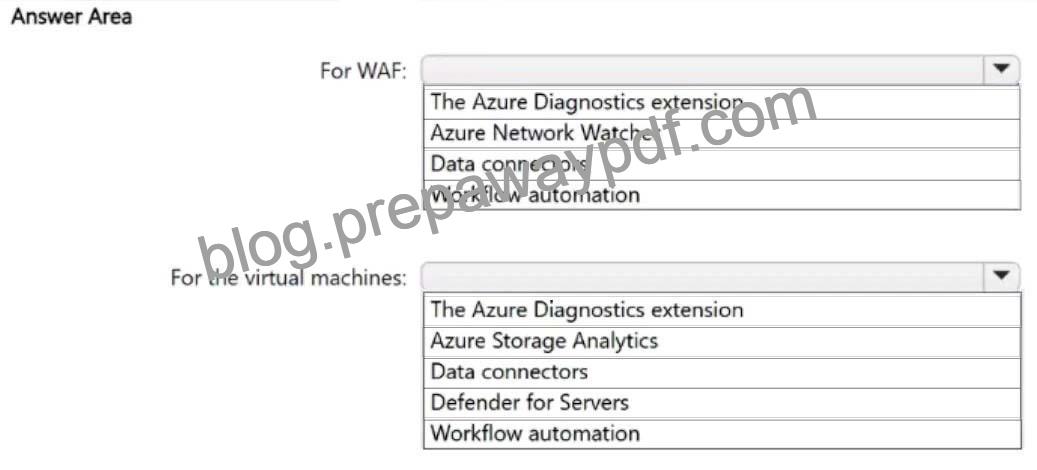
You are designing a logging and auditing solution for the proposed architecture. The solution must meet the following requirements:
– Integrate Azure Web Application Firewall (WAF) logs with Microsoft
Sentinel.
– Use Defender for Cloud to review alerts from the virtual machines.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
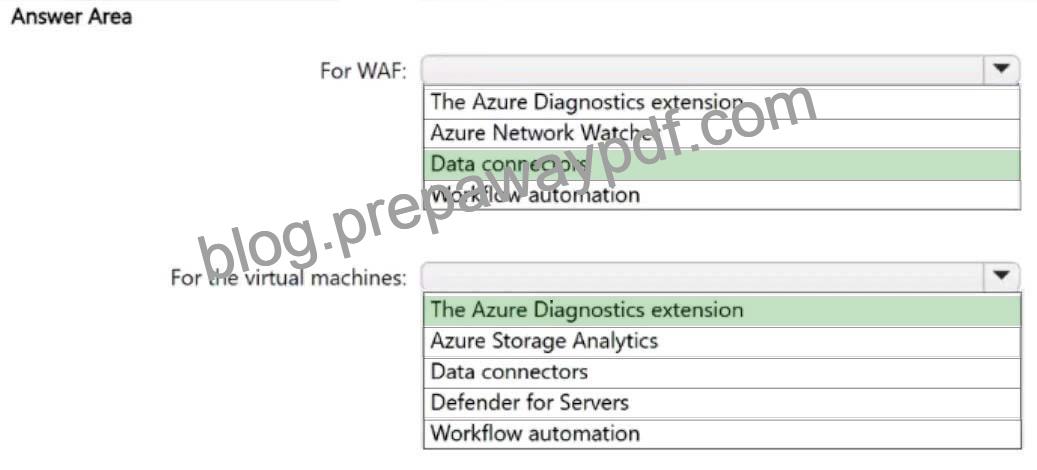
Q120. You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q121. You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q122. Your company wants to optimize using Azure to protect its resources from ransomware.
You need to recommend which capabilities of Azure Backup and Azure Storage provide the strongest protection against ransomware attacks. The solution must follow Microsoft Security Best Practices.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q123. Case Study 1 – Fabrikam, Inc
OverView
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
Existing Environment
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
– A Microsoft Entra tenant named fabrikam.onmicrosoft.com that syncs with corp.fabrikam.com
– A single Azure subscription named Sub1
– A virtual network named Vnet1 in the East US Azure region
– A virtual network named Vnet2 in the West Europe Azure region
– An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAF) enabled
– A Microsoft Sentinel workspace
– An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
– 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
– A resource group named TestRG that is used for testing purposes only
– An Azure Virtual Desktop host pool that contains personal assigned session hosts
– All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure:
– An Microsoft Entra named contoso.onmicrosoft.com
– An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications.
The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1. The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
– Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
– Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
– Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation. Machines should have a vulnerability assessment solution. All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
– ClaimsApp will be deployed to Azure App Service instances that connect to Vnet1 and Vnet2.
– Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
– ClaimsApp will access data in ClaimsDB.
– ClaimsDB must be accessible only from Azure virtual networks.
– The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
– Azure DevTest labs will be used by developers for testing.
– All the application code must be stored in GitHub Enterprise.
– Azure Pipelines will be used to manage application deployments.
– All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
– Internet-accessible applications must prevent connections that originate in North Korea.
– Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
– Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
– Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
– Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers:
– Every month, the membership of the ContosoDevelopers group must be verified.
– The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
– The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
Hotspot Question
What should you create in Microsoft Entra ID to meet the Contoso developer requirements?

Q124. Your company is migrating data to Azure. The data contains Personally Identifiable Information (Pll). The company plans to use Microsoft Information Protection for the Pll data store in Azure. You need to recommend a solution to discover Pll data at risk in the Azure resources.
What should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.

Q125. Your company has a hybrid cloud infrastructure.
The company plans to hire several temporary employees within a brief period. The temporary employees will need to access applications and data on the company’ premises network.
The company’s security policy prevents the use of personal devices for accessing company data and applications.
You need to recommend a solution to provide the temporary employee with access to company resources. The solution must be able to scale on demand.
What should you include in the recommendation?


Q126. You are designing a security operations strategy based on the Zero Trust framework.
You need to minimize the operational load on Tier 1 Microsoft Security Operations Center (SOC) analysts.
What should you do?


Q127. You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Q128. Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.

Q129. You are a security architect, and you are working with your software development team and defining a strategy for an application lifecycle management process, This process is based on the Microsoft Security Development Lifecycle Model.
What are the two phases in the threat modeling design phase?


Q130. Your company has on-premises Microsoft SQL Server databases.
The company plans to move the databases to Azure.
You need to recommend a secure architecture for the databases that will minimize operational requirements for patching and protect sensitive data by using dynamic data masking. The solution must minimize costs.
What should you include in the recommendation?


Q131. You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q132. You have a Microsoft 365 E5 subscription and an Azure subscripts You need to evaluate the existing environment to increase the overall security posture for the following components:
* Windows 11 devices managed by Microsoft Intune
* Azure Storage accounts
* Azure virtual machines
What should you use to evaluate the components? To answer, select the appropriate options in the answer area.

Q133. You have two Azure subscriptions named Sub1 and Sub2 that contain the vaults shown in the following table.

You need to design a multi-user authorization (MUA) solution for security operations on the vaults. The solution must meet the following requirements:
* RSVault1 and RSVault2 must require MUA for disabling soft delete, removing MUA protection, and disabling immutability.
* BackupVault1 and BackupVault2 must require MUA for disabling soft delete and removing MUA protection.
What is the minimum number of Resource Guard resources required?


Q134. You have an Azure subscription that contains the resources shown in the following table.

You need to recommend a network security solution for App1. The solution must meet the following requirements:
* Only the virtual machines that are connected to Subnet1 must be able to connect to D81.
* DB1 must be inaccessible from the internet
* Costs must be minimized.
What should you include in the recommendation? To answer, select the options in the answer area. NOTE:
Each correct answer is worth one point.

Q135. You have an Azure subscription that contains multiple storage accounts. The accounts contain Azure Files shares and Azure Blob Storage containers. The accounts have encryption scopes and infrastructure encryption enabled.
You need to implement customer-managed key-based encryption for the shares and the containers. The solution must ensure that the encryption keys are applied at the most granular level.
At which level should you apply the encryption keys? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q136. You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


To prepare for the Microsoft SC-100 Certification Exam, candidates should have a strong understanding of cybersecurity concepts and principles. They should also have experience in designing and implementing security solutions for organizations. Microsoft offers a variety of training and certification resources to help candidates prepare for the exam, including online courses, study guides, and practice exams.


Earn Quick And Easy Success With SC-100 Dumps: https://www.prepawaypdf.com/Microsoft/SC-100-practice-exam-dumps.html

Related Links: www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below